In the crypto world, we talk a lot about code audits, multi-sig wallets, and cold storage. We act like the biggest risks are complex mathematical exploits. But the recent security report from Binance serves as a cold bucket of water for anyone building in this space. It turns out you can have the most sophisticated automated defenses in the industry and still lose the keys because one employee wanted a better job.
The Human Firewall is Cracked
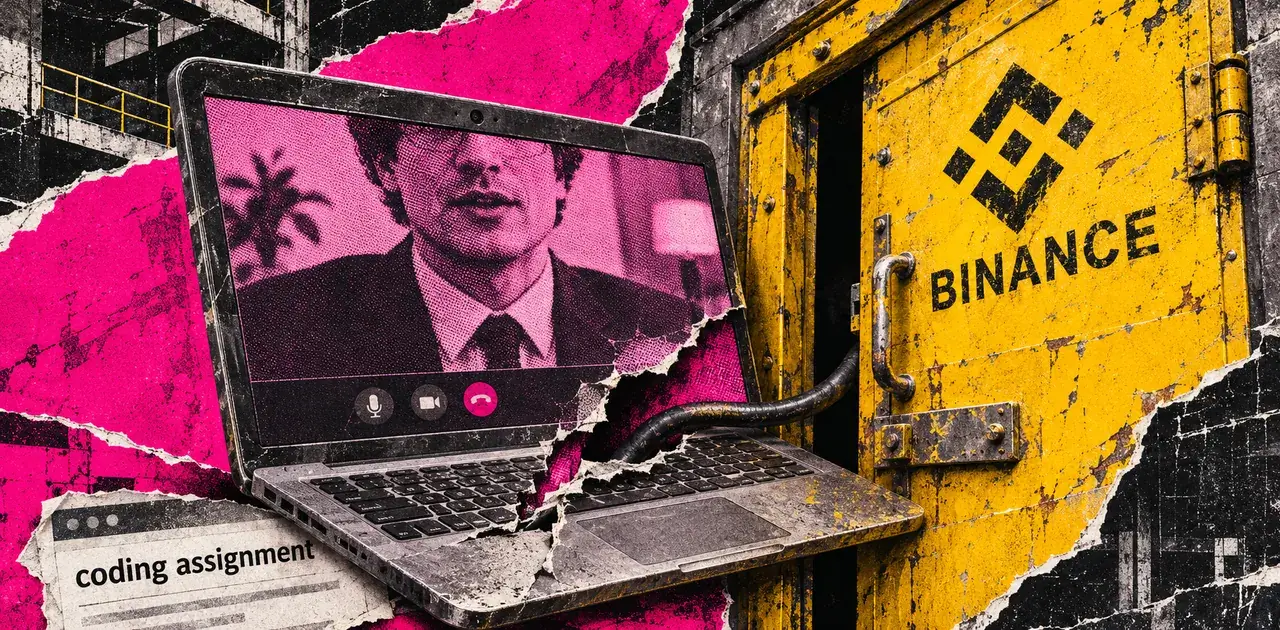
Binance recently disclosed that their security teams successfully intercepted 57 different cyber threats linked to North Korean state actors in 2024. That sounds impressive, and on a technical level, it is. Blocking state-sponsored hackers nearly five dozen times suggests their automated systems and threat intelligence are top-tier. But that success was overshadowed by a single, glaring failure: a developer fell for a fake job interview.
This is the classic Achilles' heel of the founder-led startup. We spend millions on software to keep the bad guys out, but we can't patch human curiosity or ambition. The attackers didn't need a zero-day exploit for the Binance exchange; they just needed a convincing LinkedIn profile and a malicious PDF disguised as a technical assessment.
How the Social Engineering Playbook Works
The attackers didn't just send a spam email. They played a long game. They built fake identities, staged multiple rounds of interviews, and established rapport. This is what we call social engineering, and for builders, it is significantly more dangerous than a flash loan attack. When a developer is in "interview mode," their guard is down. They want to impress. They are willing to download tools, run code snippets, or open documents that they would otherwise treat with extreme suspicion during their normal work hours.
In this specific case, the malware was delivered through the recruitment process. By the time the engineer realized the job wasn't real, the attackers already had a foothold in the system. It’s a sobering reminder that your security is only as strong as the most tired, distracted, or ambitious person on your payroll.
The $6 Billion Shadow
While Binance managed to contain the damage this time, we have to look at the broader context. These North Korean groups, often categorized under the Lazarus umbrella, are responsible for over $6 billion in stolen crypto assets over the last few years. They aren't just hobbyists; they are a well-funded, highly disciplined workforce whose entire job is to find the one crack in your armor.
For founders, this is the part that should keep you up at night. If an organization with the resources of Binance—an entity that literally tracks global flow of funds—can be compromised by a fake HR recruiter, what hope does a 10-person DeFi startup have? The answer isn't just "better software." It’s a fundamental shift in how we handle internal permissions and the "trust-but-verify" culture.
The Founder's Dilemma: Speed vs. Safety
I’ve talked to dozens of founders who complain that strict security protocols slow down their team. They hate the friction of hardware keys, restricted environments, and the inability to install third-party tools on a whim. But the Binance incident proves that friction is your best friend. If your lead dev can download a random file from a "recruiter" and execute it on a machine that has access to your production environment, you don't have a security plan. You have a ticking time bomb.
We have to stop treating security as a department and start treating it as a core cultural value. That means training your team not just on how to write clean code, but how to spot the psychological triggers that hackers use. These attackers prey on ego, urgency, and the desire for career growth.
What Builders Should Take Away
If you are building in the crypto or AI space right now, you are a target. Period. It doesn't matter if you have $10,000 or $10 billion in TVL. The Binance report highlights several critical areas where builders need to tighten up:
- Air-gapped hiring: Never allow employees to conduct interviews or download "test tasks" on machines that have access to your core infrastructure.
- Zero Trust is mandatory: No single employee should have enough access to compromise the entire system, regardless of their seniority.
- Verification protocols: If a recruiter reaches out, verify their identity through multiple channels before ever engaging in a technical discussion.
The reality is that 57 wins don't matter if you have one catastrophic loss. In the world of cybersecurity, the house doesn't always win; the hacker only has to be right once. Binance was lucky this time, but the next startup might not be.
The most dangerous piece of hardware in your office isn't the server—it's the keyboard in the hands of a person who thinks they're getting a promotion.
We need to move away from the idea that we can automate our way out of this problem. Technology can block the 57 automated attacks, but only culture and rigorous process can block the 58th attack that comes with a smile and a job offer. Stay skeptical, keep your permissions tight, and remember that in crypto, the social layer is always the most vulnerable layer.
Read the original at CryptoSlate →