I have spent years watching builders obsess over the 'Quantum Apocalypse.' It is the ultimate boogeyman in crypto. The narrative is simple: one day, a computer with enough qubits will wake up and crack the Elliptic Curve Digital Signature Algorithm that secures every satoshi on the Bitcoin network. If that happens, the game is over.
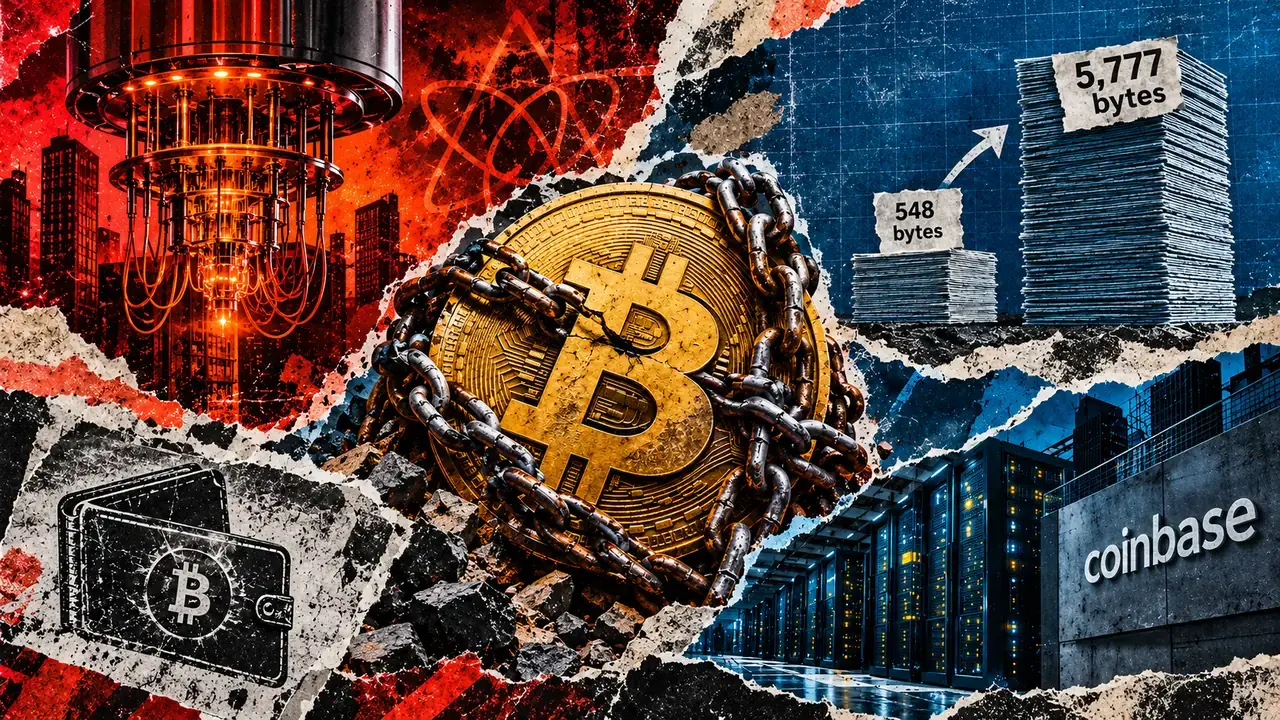
However, the real threat to Bitcoin might not be the quantum computer itself, but the cure we are trying to develop for it. Recent technical analysis into quantum-resistant signature schemes reveals a massive problem. If we switch to post-quantum cryptography today, we are looking at data footprints that are ten times larger than what we use now. For a network that already fights over every byte of block space, this is a scaling nightmare.
The Weight of Security
Bitcoin currently relies on ECDSA. It is elegant, small, and fast. But it is vulnerable to Shor’s algorithm. The leading candidates to replace it are mostly lattice-based or hash-based signature schemes. While these are mathematically 'quantum-proof,' they are physically bloated. We are moving from signatures that take up a tiny fraction of a transaction to signatures that could dominate the entire block.
When we talk about a 10x increase in data, we aren't just talking about higher transaction fees. We are talking about the fundamental decentralization of the network. If every transaction suddenly weighs ten times more, the hardware requirements to run a full node skyrocket. We already have a problem with 'initial block download' taking days for new users. Imagine multiplying that by ten. You effectively price out the home runner, leaving the network in the hands of data centers. That is not the Bitcoin most of us signed up to build.
SHRINCS and the Recovery Dilemma
One of the specific schemes being debated is SHRINCS. It is designed to be robust, keeping a larger signing path available for recovery. The logic is sound: if you lose part of your state, you need a way to get back in. But this robustness comes at a price. The data overhead is massive. From a founder's perspective, this is a classic trade-off between resilience and efficiency.
In the software world, we usually solve for speed first and edge cases later. In Bitcoin, the edge case is the entire value proposition. If you can't recover your funds, the system fails. But if the system is too heavy to run, it also fails. The SHRINCS approach highlights just how difficult it is to find a middle ground where the network remains usable for the average person while staying safe from future tech that doesn't even exist yet.
The Coordination Headache
Then we have compact signatures. On paper, these look like the winner because they keep the data size down. But there is a catch that usually gets buried in the whitepapers: they require incredibly reliable counters and airtight custody coordination. Unlike current Bitcoin signatures, where you can largely sign and forget, compact post-quantum signatures often require state management.
If you are a builder creating a non-custodial wallet or a multi-sig setup, this is a massive hurdle. You can't just have three people with hardware wallets in different cities signing a transaction whenever they feel like it. You need a synchronized state to ensure the 'counters' don't get out of whack. If the state is lost or desynchronized, the funds could be locked forever. This adds a layer of complexity to key management that makes current multi-sig look like child's play.
What This Means for Builders
If you are building on Bitcoin today, you shouldn't be panicking about quantum computers, but you should be planning for data scarcity. We are entering an era where block space will only get more expensive, regardless of quantum threats. If and when the network transitions to these larger signature schemes, the 'L2 or bust' narrative becomes a reality, not just a suggestion.
- Layer 2 is Mandatory: If L1 signatures grow by 10x, standard payments on the base layer become economically impossible for 99% of the population. Building on Lightning or other state-channel solutions isn't just an optimization; it's a survival strategy.
- State Management is the New Frontier: Wallet developers need to start thinking about how to handle stateful signing. If we end up with compact signatures to save space, the user experience will need to hide all the complex counter synchronization happening in the background.
- Efficiency over Everything: Every byte you can save in your protocol design today is a gift to your future self. The overhead is coming.
The Founder's Takeaway
The 'Quantum Threat' is often used by shills to sell new altcoins, but for Bitcoin, it is a cold, mathematical reality that requires a cold, engineering-led response. We cannot afford to be sentimental about the way Bitcoin works now if we want it to survive fifty years. However, we also cannot blindly accept 'security' updates that destroy the network's ability to run on consumer hardware.
The current state of quantum-proof signatures is not ready for prime time. They are too fat, too complex, and too demanding. For now, the best move for builders is to focus on compression and off-chain scaling. We need to build the pipes to be as efficient as possible today so that when the heavy quantum-proof water eventually starts flowing, the system doesn't burst.
Decentralization is only possible if the barrier to entry remains low. If our security measures make it impossible for a regular person to verify the chain, we haven't saved Bitcoin; we've just changed who controls it.
We need to stop looking for a 'magic pill' signature scheme and start realizing that the future of Bitcoin security is going to be a heavy, expensive, and difficult transition. The builders who win will be the ones who figure out how to hide that weight from the end user.
Read the original at CryptoSlate →