We have all been there. You are building a new DeFi integration, or maybe you are just trying to move liquidity across a few pools, and the fear of a fat-finger error or a sandwich attack hangs over your head. In the current Ethereum landscape, protecting a user from a catastrophic trade usually falls on the shoulders of the individual smart contract developer or the frontend team. If you mess up the slippage calculation, the money is gone. There is no undo button.
The Promise of EIP-7906
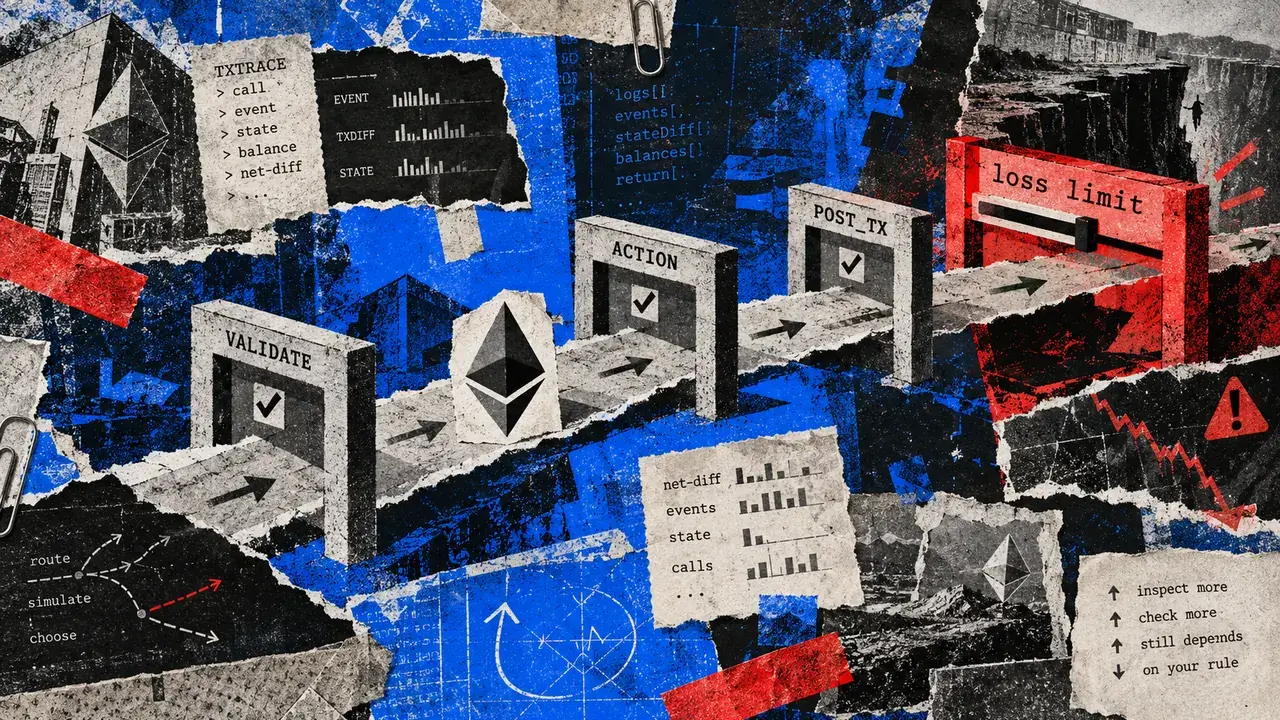
A new proposal, EIP-7906, is circulating in the developer forums. It attempts to address this by introducing formal safety checks within the execution layer. The goal is simple: allow a transaction to specify its own boundaries. If a trade results in a loss that exceeds a certain threshold, the transaction should theoretically revert before the damage is done. On paper, it sounds like the seatbelt Ethereum has needed for a decade.
But as someone who has spent years looking at how these systems actually fail in the wild, I am skeptical. The current draft of EIP-7906 relies on a mechanism where the outcome checks are essentially defined during the transaction build process. This creates a circular dependency that most builders should be wary of. If the safety check is only as strong as the code defining it, and that code is subject to the same vulnerabilities as the trade itself, are we actually safer?
The Problem with Local Limits
The core issue here is who sets the loss limit. In the current proposal, the logic for determining what constitutes a 'bad trade' often originates from the same builder or automated system creating the transaction. If an attacker manages to manipulate the input parameters or the price oracles that a builder relies on, they can just as easily manipulate the safety check parameters.
For a safety check to be meaningful, it needs to be decoupled from the immediate transaction logic. It needs to be a policy, not just another variable. When a builder allows the transaction to define its own ceiling for pain, they are effectively asking the fox to guard the henhouse. If a malicious actor can influence the transaction construction, they can widen the loss limit until the safety check becomes decorative.
Why Builders Should Care
If you are building in the Ethereum ecosystem, you know that user trust is the hardest thing to earn and the easiest thing to lose. We have seen countless protocols drained because of small logic errors in how they handle state changes. EIP-7906 is a step toward making the network 'aware' of financial risk, but it places a massive burden on the developer to get the policy right.
- Increased Complexity: Adding these checks requires more gas and more complex state management.
- False Sense of Security: Builders might become lazy with their own internal validation, assuming the EIP-7906 check will catch everything.
- Oracle Dependency: If your safety check relies on a price feed, and that feed is manipulated, your safety check is useless.
The Policy vs. Transaction Debate
The real conversation we should be having isn't about whether we need safety checks—we obviously do—but where those checks live. A truly robust system would involve policies that the transaction builder cannot weaken. Imagine a scenario where a wallet or a smart account has a hard-coded limit that exists outside the scope of individual transaction payloads.
Right now, EIP-7906 feels like a tool for sophisticated builders to protect themselves against their own mistakes, but it doesn't necessarily protect the end user from a sophisticated attacker who understands the builder's logic better than the builder does. For founders, this means you can't just 'plug in' this EIP and assume your users are safe. You still need to architect your systems with the assumption that every input is a potential lie.
The biggest risk in crypto isn't the code we haven't written yet; it is the assumptions we make about the code we have already shipped.
The Founder Perspective
From a founder’s perspective, I look at EIP-7906 and see a double-edged sword. On one hand, anything that moves us closer to a world where a single bad trade doesn't bankrupt a user is a win. On the other hand, we are adding more layers of abstraction to a stack that is already leaning.
If you are running a team, your directive shouldn't be to wait for these EIPs to save you. You need to be building your own 'circuit breakers' today. Don't wait for the protocol to give you a safety net. The most successful builders I know are the ones who treat the Ethereum execution layer as a hostile environment, regardless of what safety checks are proposed.
Takeaway for the Road
EIP-7906 is a noble effort, but in its current form, it is a suggestion, not a law. As long as the financial limits can be weakened by the same entity building the transaction, the door remains cracked open for exploits. For those of us in the trenches, the lesson remains: trust the math, but never trust the parameters without a secondary, independent source of truth. If the safety check can be bypassed by the person it's meant to protect, it isn't a safety check—it's just more code to audit.
Read the original at CryptoSlate →