In crypto, we talk a lot about 'code is law,' but we often forget that liquidity is the judge. This week provided a masterclass in the price of impatience. A group of hackers, reportedly linked to the massive 2022 BNB Chain exploit, attempted to move their stolen assets through the Ethereum ecosystem. They didn't just pay a fee; they practically donated $119 million to the network's participants.
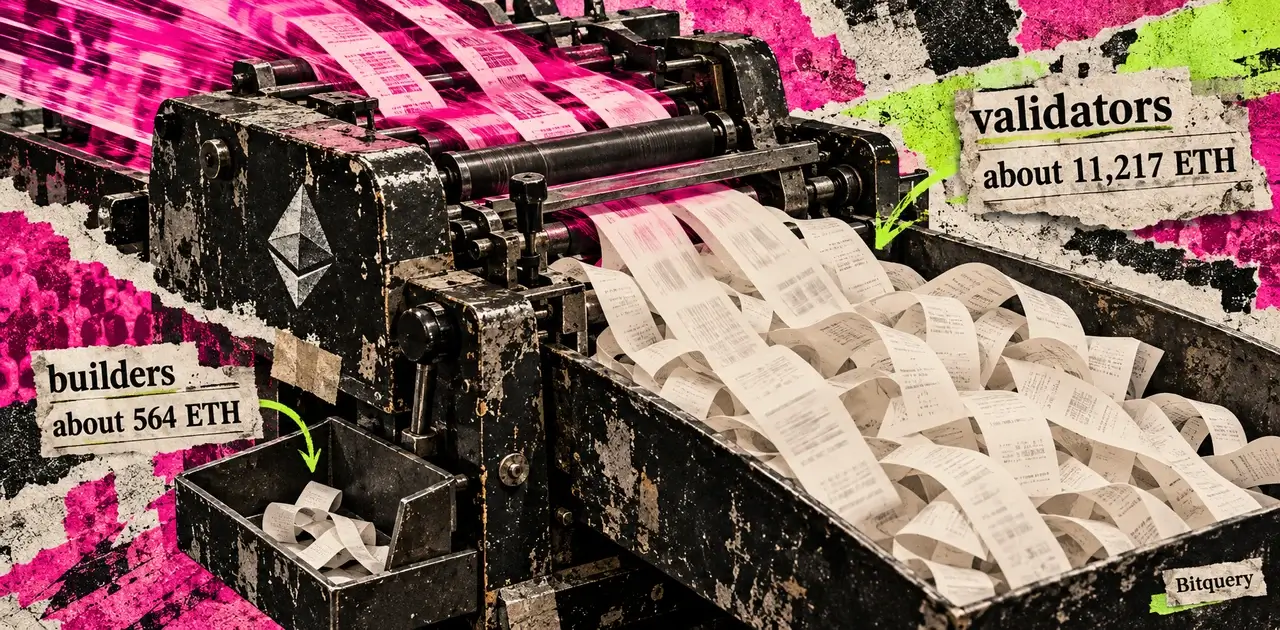
Bitquery recently analyzed these transactions, and the math is staggering. Over a four-hour window, the hackers lost over $119 million in value due to slippage and MEV. Of that, roughly $30 million—about 11,217 ETH—went directly into the pockets of the validators who proposed the blocks. This wasn't a mistake in the smart contract; it was a mistake in the execution.
The Cost of Urgency
When you are trying to launder millions in stolen crypto, you are playing a game against the clock. The hackers were trying to swap large quantities of USDT for ETH. In a normal market environment, you'd execute this over days or weeks using small batches to minimize price impact. These hackers didn't have that luxury. They slammed the market with massive orders, causing the price of the assets they were buying to skyrocket while the price of what they were selling plummeted.
For builders, this is a clear lesson in how DeFi plumbing works under pressure. The hackers used decentralized exchanges (DEXs) where the price is determined by the ratio of assets in a pool. By dumping such a massive volume into these pools so quickly, they essentially created a massive arbitrage opportunity. They were selling at a deep discount, and the network was more than happy to take the other side of that trade.
Validators and the MEV Windfall
What is particularly interesting here is the distribution of the 'slippage.' While the hackers lost $119 million in total value, the validators were the ones who saw the most direct benefit. In the Ethereum ecosystem, the person who proposes a block has a lot of power over which transactions get included and in what order. Through MEV (Maximal Extractable Value), bots and builders can capture the price discrepancies created by large, inefficient trades.
Bitquery's data shows that while builders kept around 564 ETH, the lions' share—over 11,000 ETH—went to the validators. This highlights a power dynamic in the current Ethereum architecture. When the market becomes volatile or when someone makes a massive mistake, the infrastructure providers are the ones who get paid. It is a highly profitable time to be running a node, provided you are in the right place at the right time.
The Founder's Perspective: Security vs. Scalability
As founders, we often focus on making our protocols faster or cheaper. But stories like this remind us that the 'inefficiency' of the blockchain is sometimes its most robust feature. If the hackers could have moved this money instantly and without trace, the ecosystem would be more dangerous. Instead, the very nature of on-chain liquidity acted as a friction point. It didn't stop the crime, but it certainly taxed the criminals.
However, there is a flip side to this. This $30 million windfall for validators is essentially a tax on the network's liquidity. While it is easy to cheer because it happened to a 'bad actor,' the same mechanisms can punish legitimate users who aren't careful with their slippage settings or who find themselves in a low-liquidity environment. If we want to build products for the next billion users, we have to find ways to protect them from this kind of value extraction.
What This Means for the Future of MEV
The fact that validators walked away with such a massive sum will likely reignite the debate around MEV redistribution. Currently, if a whale (or a hacker) makes a mistake, the validator gets a bonus. There are ongoing discussions in the developer community about how to make this 'fairer'—perhaps by burning a portion of this excess value or redistributing it to the users who were impacted.
The transparency of the blockchain is a double-edged sword. It allows us to track the thieves, but it also allows the sharks to see the blood in the water and react in milliseconds.
We are seeing the rise of 'MEV-aware' applications that try to shield users from these effects. As a builder, if you aren't thinking about how MEV impacts your end-user, you are leaving them vulnerable. The hackers' $119 million loss is an extreme example, but micro-versions of this happen every single day to retail traders.
A Reality Check on Decentralization
Some might look at this and say the system worked. The hackers were penalized by the very system they tried to exploit. But others will see $30 million going to a handful of validators as a sign of centralization and 'rent-seeking' behavior. Both can be true at the same time.
The takeaway for the rest of us is simple: execution matters as much as the code. You can have the most secure smart contract in the world, but if your users (or your attackers) don't understand the liquidity dynamics of the pools they are interacting with, the network will extract its pound of flesh. In this case, the Ethereum network just happened to take $119 million worth of flesh.
Don't expect this to be the last time we see a 'fat finger' or a 'rushed trade' result in a validator windfall. As long as there is high-velocity money moving through decentralized pipes, there will be someone at the end of the line ready to catch the overflow. For builders, the goal should be to make those pipes more efficient, even if it means the validators have to find their profits elsewhere.
Read the original at CryptoSlate →