The Cost of Lessons Learned
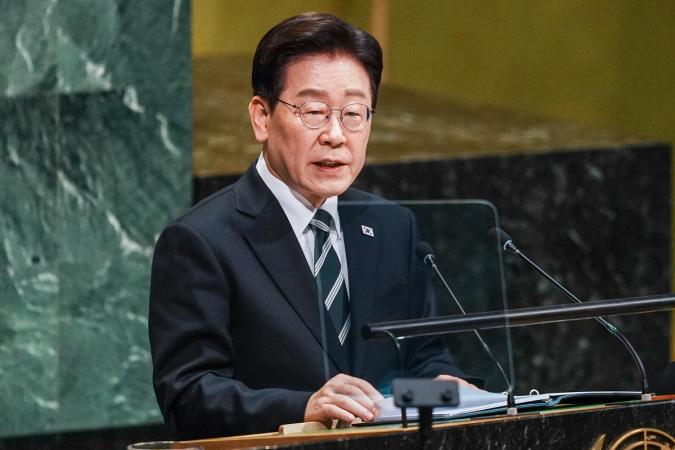
In the wake of a $6.3 billion breach affecting Binance, the largest centralized exchange in the space, South Korea is hitting the panic button. President Lee Jae Myung is now calling for the appointment of a national cybersecurity czar. It is a reaction we have seen before in traditional finance, but the scale of this specific loss has forced a realization that current defensive structures are nowhere near robust enough for the modern era.
For those of us building in this space, this is more than just another headline about a hack. It is a signal that the era of fragmented security is ending. When billions of dollars vanish in a single event, governments stop treating crypto as a fringe experiment and start treating it as a national security threat. The South Korean proposal is to create a government-wide agency that coordinates defense across financial institutions and critical infrastructure, specifically focusing on the new threats posed by the integration of AI.
The AI X-Factor in Security
The core of Lee Jae Myung’s argument rests on the idea that AI has fundamentally changed the offensive capabilities of bad actors. We are no longer just looking at manual social engineering or simple code exploits. We are looking at automated, intelligent systems that can probe for vulnerabilities at a speed human dev teams cannot match. When you combine the speed of AI with the finality of blockchain transactions, you get a recipe for the kind of disaster we just witnessed with the Binance exploit.
The South Korean government’s pivot toward a centralized czar suggests they believe the solution is a unified front. In the current landscape, a bank has one set of protocols, an exchange has another, and the power grid has a third. If you are a builder, you know that these systems are increasingly interconnected. A vulnerability in a specific oracle or a bridge can bleed into the broader financial system. Lee’s proposal is an attempt to map these dependencies before the next multi-billion dollar hole is ripped in the economy.
What This Means for the Founder Perspective
If you are a founder, the move toward a state-mandated security czar is a double-edged sword. On one hand, standardized protocols and better intelligence sharing could save your project from a catastrophic zero-day exploit. On the other hand, we are looking at the potential for heavy-handed regulation that could stifle the very speed that makes this industry competitive. We have to be honest: the reason these hacks keep happening is that we often prioritize ship speed over rigorous, adversarial testing.
I have always maintained that security is not a feature; it is the foundation. If South Korea follows through with this, expect other jurisdictions to follow. We are likely looking at a future where your project will not just be audited by a private firm, but will need to meet specific, state-level cybersecurity criteria to operate in major markets. This is the price of institutional adoption. You cannot ask for trillions in capital to flow into the ecosystem without expecting the entities responsible for that capital to demand a seat at the security table.
Moving Past Fragmented Defense
The current model of security in crypto is reactive. Something breaks, a post-mortem is written, and we all try to learn from the mistake. The $6.3 billion Binance incident proves that the "move fast and break things" mentality has hit a hard ceiling. You cannot "break" $6.3 billion without causing systemic damage to trust. The South Korean response is a clear indicator that the threshold for acceptable loss has been crossed.
- Increased Oversight: Expect mandatory reporting of even minor breaches to a central authority.
- AI-Driven Defense: A push for projects to use the same level of AI sophistication in their defense as attackers use in their exploits.
- Infrastructure Focus: A shift in focus from just securing the "coins" to securing the underlying nodes, bridges, and data centers.
The Skeptical Take
While a cybersecurity czar sounds good on paper, we should be skeptical of how much a centralized government agency can actually do against decentralized threats. Governments are notoriously slow. By the time a new regulation is drafted, the exploit kits have already evolved. There is a risk that this new agency becomes a bureaucratic hurdle rather than a genuine shield.
However, the focus on AI is the correct move. We are seeing a shift where code is writing code, and by extension, bugs are finding bugs. If a national agency can facilitate real-time threat intelligence sharing between the private sector and the state, that is a net win. But if it just becomes another layer of red tape for founders to navigate, we will see talent and liquidity move to regions with more pragmatic approaches.
Takeaway for Builders
The lesson here is simple: the margin for error is now zero. As AI makes attacks more efficient, your security budget and time allocation must scale accordingly. Do not wait for a government czar to tell you how to secure your stack. The South Korean move is a warning shot to the entire industry that the days of self-regulation regarding security are numbered. If we don’t get our house in order, the state will do it for us, and we probably won’t like their methods.
"When billions disappear, the conversation shifts from innovation to preservation. South Korea's call for a cybersecurity czar is the first of many attempts by states to reclaim control over a volatile digital landscape."
We need to stop looking at these hacks as isolated incidents and start seeing them as the catalyst for a total overhaul of how we build. If your roadmap doesn't include a significant pivot toward AI-resilient security, you are building on sand. The Binance hack wasn't just a loss for one exchange; it was the starting gun for a new era of state-monitored digital finance.
Read the original at CoinDesk →