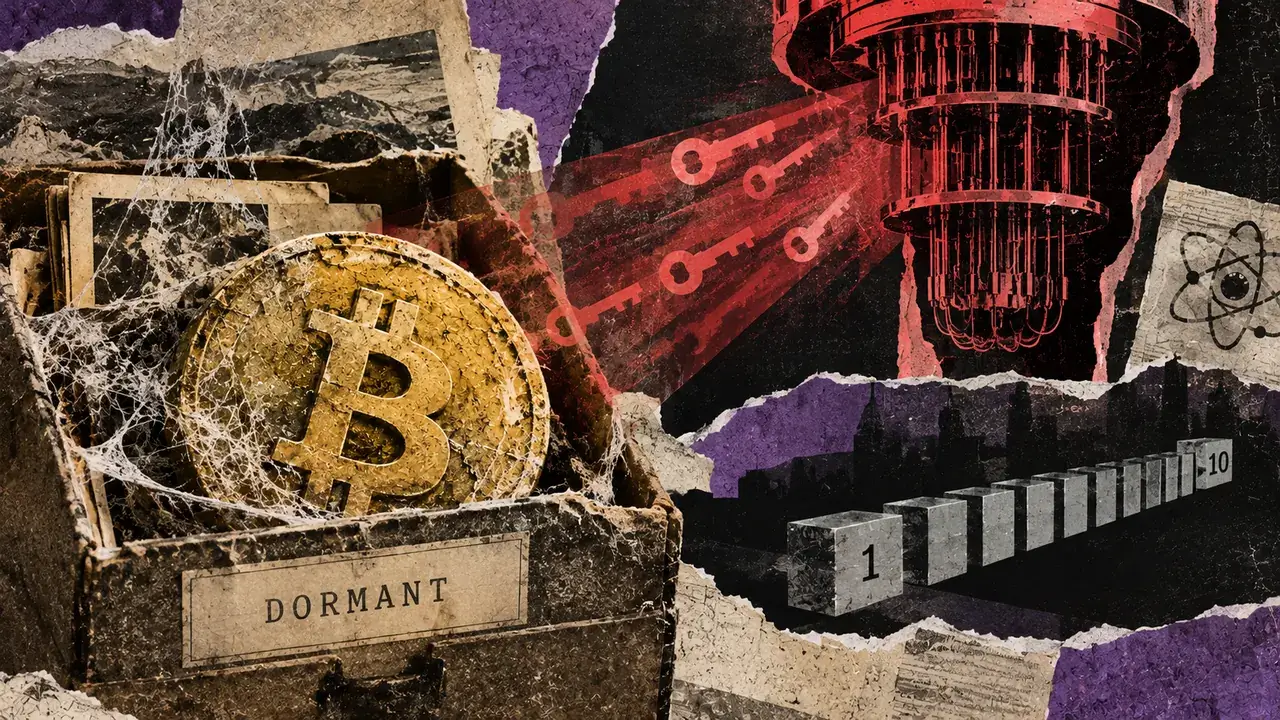
We have all heard the doom-and-gloom scenarios about quantum computers. The narrative usually goes something like this: a massive machine in a basement somewhere finally turns on, runs a specific algorithm, and suddenly every private key on the Bitcoin network is as transparent as a glass window. While the timeline for this is still debated, the math is settled. Traditional elliptic curve cryptography, the stuff Bitcoin relies on, isn't built to withstand a sufficiently powerful quantum adversary.
But the real problem isn't the math. We already have post-quantum cryptography (PQC) candidates that can resist these attacks. The real headache, and the one that should keep builders up at night, is the migration. How do you move an entire decentralized network to a new security standard without accidentally robbing the very people you are trying to protect?
The Vulnerability of the Idle
Nic Carter recently revisited a hypothetical scenario that highlights a massive flaw in our current transition plans. Bitcoin isn't just a collection of active traders; it is a massive graveyard of lost coins, long-term cold storage, and forgotten wallets. A large portion of the circulating supply sits in addresses that haven't moved in a decade.
If we decide to implement a mandatory upgrade to quantum-resistant signatures, we face a paradox. If we allow old, non-quantum-resistant addresses to keep spending, a quantum attacker can simply wait for an owner to broadcast a transaction, intercept it, and use a quantum computer to derive the private key before the original transaction is even confirmed. If we force everyone to migrate to new addresses by a certain deadline, any user who missed the memo—or who lost their keys in a way that requires the old format—is effectively wiped out.
The P2PK Problem
The most at-risk coins are the oldest ones. In the early days, Bitcoin used Pay-to-Public-Key (P2PK). In these transactions, the public key is literally sitting there in the script for everyone to see. A quantum computer doesn't even need to wait for a transaction to be broadcast; it can just scan the UTXO set and start cracking keys at its leisure. This includes Satoshi’s original coins.
Newer formats like P2PKH (Pay-to-Public-Key-Hash) are slightly safer because the public key is hidden behind a hash until the owner tries to spend the coins. However, the moment you hit "send," that public key is revealed to the mempool. In a quantum world, that brief window is all an attacker needs to front-run you.
The Founder's Dilemma
For those of us building in this space, this isn't just a technical hurdle. It is a philosophical crisis. Bitcoin’s core value proposition is the immutability of ownership. If the protocol developers implement a hard fork that invalidates old addresses, they are essentially performing a soft-confiscation of property.
If you are a founder building a wallet or a custody solution, you have to ask: how do we verify the identity of a legacy holder without compromising the decentralized nature of the network? If we require a "proof of ownership" that involves a manual reveal of the old key, we are creating a honeypot for attackers. If we do nothing, we leave the network’s integrity up to the speed of quantum hardware development.
The Lockout Risk
The most likely path forward involves a "grace period" where users can migrate their funds to new quantum-secure addresses. But here is the catch: many people physically cannot migrate. There are billions of dollars worth of Bitcoin held in multisig setups where one of the signers has passed away, or in time-locked contracts that won't open for years.
If the network moves to a new standard and shuts the door behind it, those legitimate owners are locked out. We would be solving a security problem by creating a mass-extinction event for legacy capital. That is a hard pill for the community to swallow, and it would likely lead to a contentious chain split.
Building for the Long Game
What does this mean for developers today? It means we need to stop treating quantum resistance as a "sometime in the 2030s" problem. We need to start thinking about abstraction layers now. If we can build systems that allow for modular signature schemes, we can transition more smoothly when the time comes.
- Account Abstraction: This is a major area of hope. By moving away from hard-coded ECDSA and toward programmable accounts, we give users a way to rotate their security models without needing to move funds to entirely new addresses.
- Hybrid Signatures: We should be looking at ways to combine traditional signatures with PQC signatures. This adds overhead, but it creates a double-layered defense that protects against both classical and quantum threats.
- Soft-forking Migrations: Instead of a hard cut-off, we need to design mechanisms that allow legacy coins to be "burned" and "minted" into a new quantum-secure layer through a verifiable process that doesn't rely on a central authority.
A Reality Check
I’m skeptical of the people who say quantum computers will kill Bitcoin tomorrow. I’m equally skeptical of the people who say it’s a non-issue. The reality is that the fix exists, but the implementation is a social and logistical nightmare.
As builders, we shouldn't be focused on the scary "quantum apocalypse." We should be focused on the user experience of the transition. The first projects that figure out how to bridge the gap between legacy security and the quantum future—without losing user funds in the process—are the ones that will win the trust of the market.
The threat isn't just the hacker with a quantum computer; it's the developer who forgets that Bitcoin's biggest strength is the people who bought in ten years ago and walked away.
We cannot leave the pioneers behind just to check a security box. The challenge isn't just writing better code; it's maintaining the social contract of Bitcoin while the underlying math changes beneath our feet. If we fail at that, the quantum computer won't need to crack our keys—we will have already broken the network ourselves.
Read the original at CryptoSlate →