Cybersecurity used to be a game of cat and mouse played between human attackers and defensive teams. Those days are gone. We are now entering the era of industrial-scale phishing, and Microsoft’s recent takedown of a massive fraud network shows us exactly how the machinery works. This isn't just about stolen passwords; it is about how stablecoins and automation have created a professionalized supply chain for crime.
The Scale of the Breach
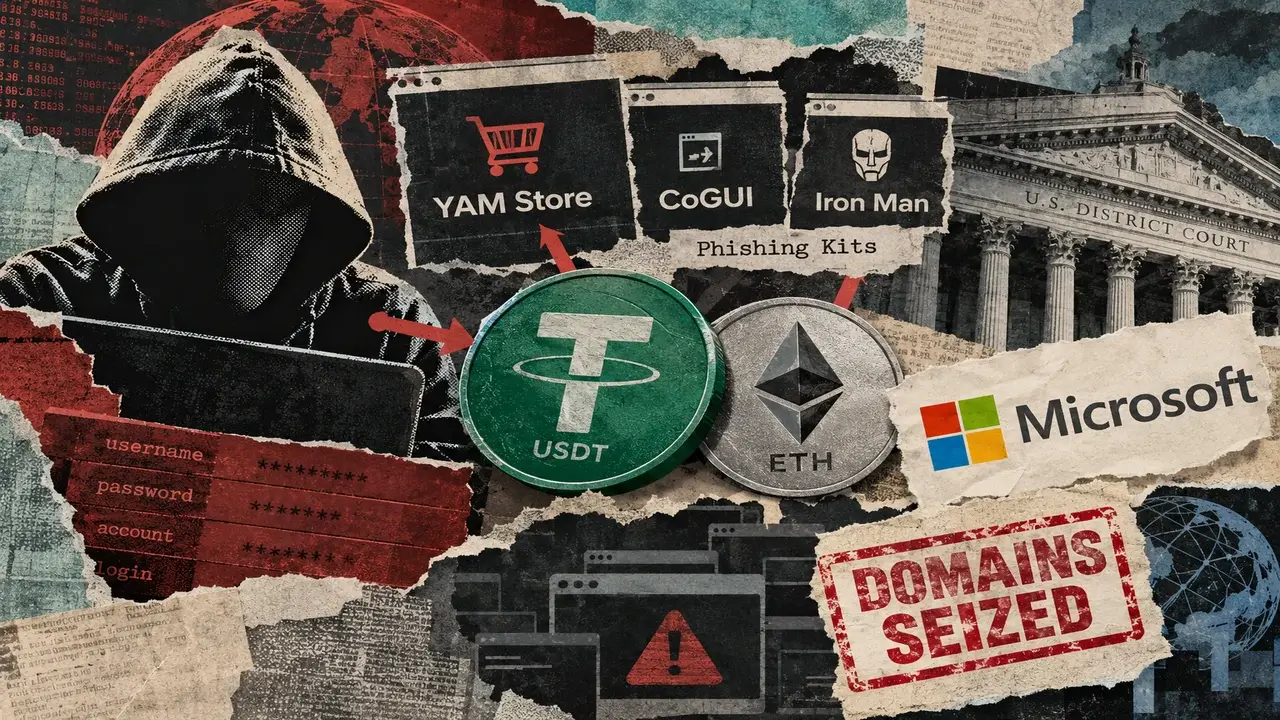
Microsoft’s threat intelligence team recently exposed a network that targeted over 75,000 organizations. Let that number sink in. This wasn't a targeted hit on a few high-value banks. This was a dragnet designed to catch anyone and everyone. The operation relied on a service known as the YAM Store, a marketplace where attackers could buy phishing kits, stolen credentials, and the infrastructure needed to launch massive campaigns.
By seizing domains and shutting down accounts, Microsoft has disrupted the immediate flow of traffic, but the underlying mechanics should worry anyone building in the digital space. The attackers weren't just using the cloud to host fake login pages; they were using Tether (USDT) to fund the entire operation. This provides a level of friction-less, cross-border settlement that traditional banking simply can't match, allowing these groups to scale faster than ever before.
The Professionalization of Phishing
For founders and developers, the key takeaway here is the "as-a-service" model. We often think of hackers as lone wolves sitting in dark rooms. The reality is much closer to a SaaS startup. One group builds the phishing kit (the software), another group hosts the infrastructure (the platform), and another group provides the financial rails (USDT).
The YAM Store functioned as a central hub. It allowed low-skill attackers to purchase high-quality tools. This lowers the barrier to entry for cybercrime to almost zero. If you have a few hundred dollars in USDT, you can buy a kit that mimics a corporate login page perfectly, bypasses basic multi-factor authentication, and automates the harvesting of data.
Why USDT is the Fuel
We talk a lot about the benefits of stablecoins for the unbanked or for cross-border trade. But we have to be honest about why they are the preferred tool for these networks. USDT offers instant liquidity without the need for a legacy bank account that can be easily flagged or frozen by a local branch manager.
While Tether has cooperated with law enforcement in the past to freeze assets, the decentralized nature of how these kits are sold makes it hard to play whack-a-mole. By the time one wallet is flagged, ten more have been created. For the operators of the YAM Store, crypto isn't a speculative asset; it’s a utility for operating outside the reach of traditional financial oversight.
What This Means for Builders
If you are building a platform, you are a target. It doesn't matter if you are a small DeFi protocol or a mid-sized B2B software company. These automated kits don't care about your mission statement. They are looking for vulnerabilities in your users.
- Identity is the new perimeter: Traditional firewalls are useless when your employees or users willingly hand over their credentials to a fake site. Builders need to move toward hardware-based keys and passkeys that are resistant to phishing.
- The cost of automation: We are using AI and automation to build better products, but the bad guys are using them to find holes in those products. If 75,000 organizations can be hit in a single campaign, your security posture needs to be as automated as the attacks.
- Compliance is coming for the rails: As more reports link USDT to large-scale infrastructure for crime, expect the regulatory heat on stablecoin issuers to intensify. If you rely on these assets for your business logic, have a plan for increased scrutiny.
The Myth of the Unstoppable Network
Microsoft’s intervention—domain seizures and account shutdowns—proves that these networks aren't invisible. They leave trails. The problem is that the cleanup happens after the damage is done. For the thousands of organizations that had their data compromised, the seizure of a few domains is cold comfort.
We see this cycle constantly in crypto and tech. A new tool emerges, it gets weaponized, and the industry reacts. But the speed of the YAM Store operation suggests we are falling behind. When an attacker can spin up a global phishing campaign for the price of a mid-range laptop, the defensive side has to stop thinking about individual incidents and start thinking about systemic resilience.
The goal of modern security isn't just to stop the attack, but to make the cost of the attack higher than the potential reward.
Right now, the math favors the attackers. USDT and automated kits have made the cost of attacking 75,000 companies incredibly low. Until we change that fundamental economic equation—through better identity standards and more aggressive infrastructure defense—this is just the beginning of the industrial phishing era.
The Takeaway
The Microsoft report isn't just a news story about a hack; it is a map of the new shadow economy. As builders, we have to recognize that the same tools we love—programmable money and scalable infrastructure—are being used to dismantle the trust we are trying to build. Stop relying on passwords, start watching your network's financial footprints, and don't assume you're too small to be noticed. In a world of automated phishing, everyone is a target.
Read the original at CryptoSlate →