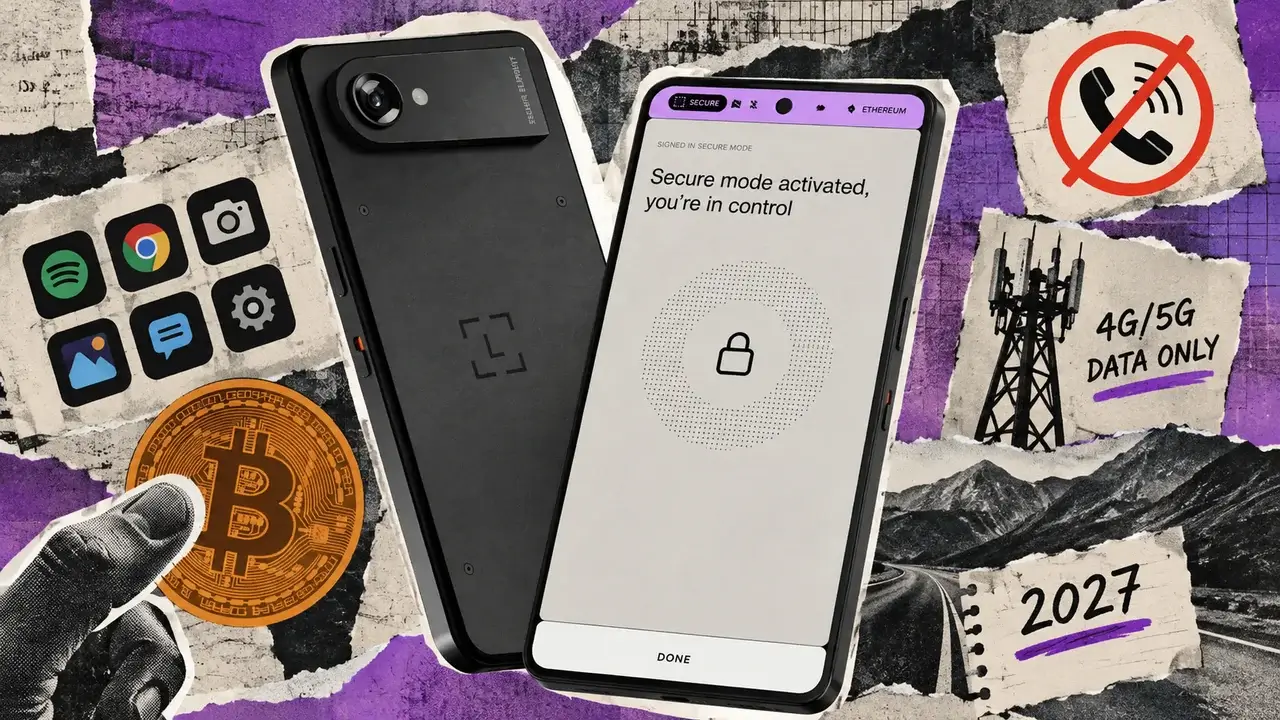
Hardware wallets used to be the final word in security. You bought a USB stick, scribbled down some words on a piece of paper, and felt like a digital fortress. But the landscape has shifted. We are seeing more reports of compromised devices, clever social engineering, and a growing realization that even cold storage has a melting point. Now, Ledger is asking the market to double down on a new $849 device called the Flex, aiming for a 2027 delivery. As a founder, I look at this and see a massive bet on a future that might not exist by the time the product actually ships.
The Trust Paradox in Cold Storage
The core problem with hardware wallets today isn't just the code; it is the human element and the supply chain. Ledger has had its share of public relations headaches, from the 2020 database leak to the controversial Recovery service that sparked a debate about backdoors. When a company asks for nearly a thousand dollars for a device that won't arrive for three years, they aren't just selling hardware. They are selling a promise of future relevance.
For builders, the challenge is clear: how do we convince users that their assets are safe when the very tools meant to protect them are under constant fire? The $849 price tag is a signal. It is an attempt to move away from the 'tech toy' category and into high-end enterprise security. But in crypto years, 2027 is an eternity. We might be three cycles ahead by then, and the idea of a physical device for signing transactions could be as obsolete as a pager.
The Reality of compromised wallets
We need to talk about why people are losing money even with hardware wallets. It is rarely a brute-force attack on the chip itself. It is usually a failure in the interface. Criminals are getting better at tricking users into signing malicious permissions. Ledger’s new pitch involves a data-only device that pairs apps with hardware approvals, trying to bridge the gap between usability and isolation.
But here is the skeptic's take: every new feature is a new attack vector. Adding a touchscreen, Bluetooth, or complex app integrations creates more surface area for exploits. If you are building in the security space, your goal shouldn't be to add more 'stuff.' It should be to remove every possible point of failure. High-priced luxury hardware feels like a distraction from the fundamental need for simpler, more transparent open-source standards.
Why the 2027 Timeline is a Risk
I have seen too many projects in the AI and crypto space fail because they built for the present and ignored the rate of change. By 2027, account abstraction will likely be the standard. We will have smart contract wallets that don't require a physical seed phrase to be tucked under a mattress. We will have biometric security layers that make a $849 plastic rectangle look like a relic.
If you are a founder, don't look at Ledger's high-ticket item as a blueprint for success. Look at it as a case study in market positioning. They are trying to lock in their most loyal (and wealthiest) users now, before the underlying technology of 'wallets' shifts entirely toward software-defined security. The risk for the consumer is paying for a premium solution that might be technically 'secure' but practically useless in a future of automated AI agents and seamless chain abstraction.
The Builder Perspective: Security vs. UX
We are stuck in a cycle where security feels like a chore. The industry has spent a decade telling users that if they don't have a hardware wallet, they are doing it wrong. But as these devices become more complex and expensive, we are excluding the very people we need for mass adoption. A builder's priority should be making security invisible, not making it an $800 luxury purchase.
Ledger is betting that there will always be a segment of the market that equates price with protection. Maybe they're right. But the smarter move for developers is to look at how we can achieve the same level of safety through decentralized identity and multi-party computation (MPC) without requiring users to wait three years for a shipment from France.
The goal is not to build a better vault; the goal is to make the vault unnecessary.
We have to ask if we are solving for the user or for the manufacturer's bottom line. When I see a pre-order for a device that costs as much as a new iPhone but doesn't ship until 2027, my skepticism hits a peak. In a world where AI can now identify vulnerabilities in smart contracts in seconds, our hardware needs to be more than just a fancy screen. It needs to be an active participant in our security, not a passive gatekeeper.
The Takeaway for the Ecosystem
The takeaway here isn't just about one company or one device. It's about the shift in how we perceive digital ownership. We are moving away from the era of 'don't trust, verify' and into an era of 'prove you can protect me.' Ledger's move is a defensive one, trying to reclaim the trust they lost during previous controversies by offering a high-end, premium alternative.
For the rest of us, the path forward is clear. We need to focus on building systems that don't rely on the user being a security expert. We need protocols that can detect a compromise before the transaction is even broadcast. If the only way to stay safe is to spend $849 and wait three years, then crypto has failed its most basic promise of financial sovereignty for all. Keep your eyes on the tech, not the price tag. The real innovations won't come in a box; they'll come in the code.
Read the original at CryptoSlate →