We have reached the inevitable stage of the crypto regulatory cycle: the cleanup phase. For the last year, the Markets in Crypto-Assets regulation, or MiCA, was held up as the gold standard for clarity. It promised a unified framework for 27 countries, offering a holy grail for founders: the ability to get licensed in one EU member state and then passport those services across the entire bloc. It was efficient, or so we thought.
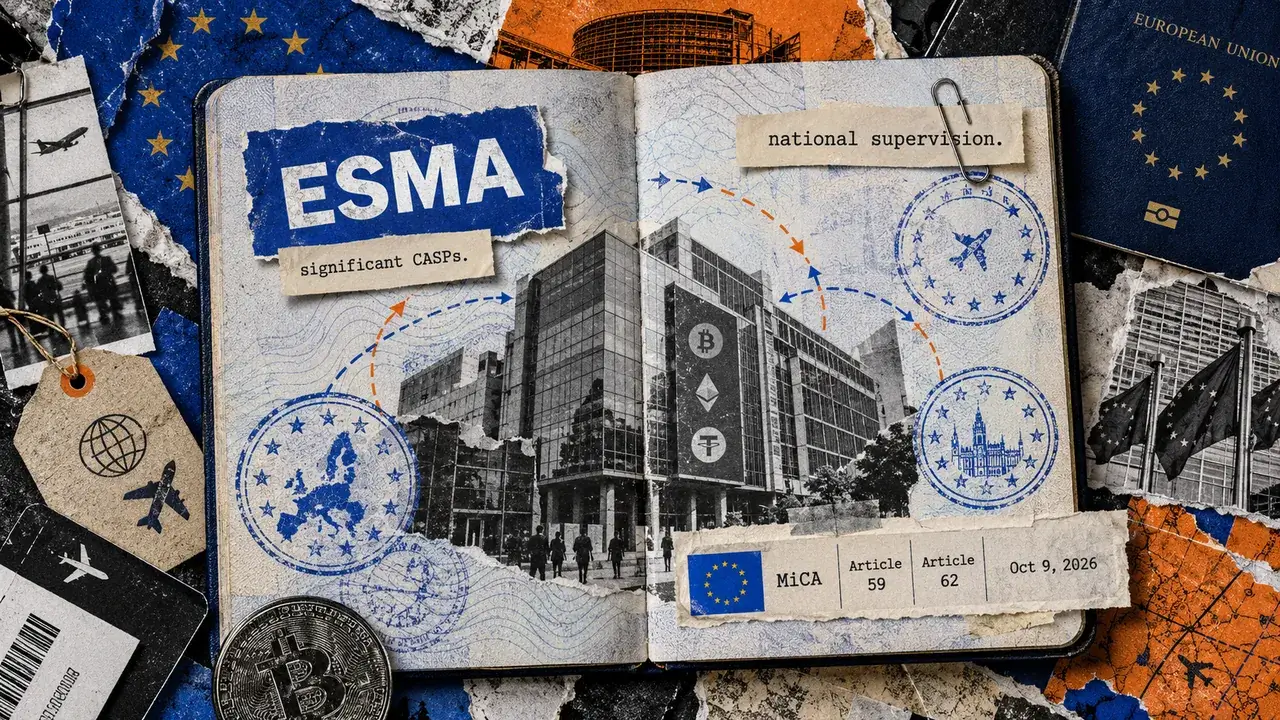
Now, the European Council is looking at the fine print. They have identified what they are calling a loophole in the cross-border supervision model. The concern is that large-scale exchanges are using a single national license to operate in dozens of jurisdictions where the local regulator has zero oversight of their activity. Regulators don't like gaps, and they are moving to close this one by shifting power toward the European Securities and Markets Authority, or ESMA.
The Passporting Paradox
For a builder, the passporting rule was the biggest selling point of MiCA. If you were a founder based in France or Lithuania, you could deal with your local regulator, get your paperwork in order, and legally offer your platform to customers in Germany, Italy, and Spain without filing 26 other applications. It leveled the playing field for startups trying to compete with US giants.
But from a regulator's perspective, this created a blind spot. A company could theoretically pick the member state with the most lenient enforcement or the smallest staff, get approved, and then become a systemic risk for the entire continent. The Council is now proposing a selective ESMA model. This would essentially cherry-pick the largest, most influential crypto service providers and place them under direct EU-level supervision, rather than leaving them to national authorities.
Why This Matters for Founders
If you are building a small DEX or a localized wallet, this might not hit your radar today. But if you have ambitions for scale, the goalposts are moving. The shift toward ESMA supervision means that once you hit a certain threshold of users or volume, you aren't just dealing with a local office anymore. You are dealing with the central European authority.
This adds a layer of complexity that many founders aren't prepared for. National regulators are often more accessible; you can build a relationship with them. ESMA is a different beast. Their oversight is designed to be rigid and uniform. For a founder, this means your compliance costs aren't just a one-time setup fee—they are a scaling tax that grows as your business grows.
The End of Regulatory Arbitrage
We’ve seen this play out in traditional finance for decades. Banks often shop for the friendliest jurisdiction to call home. In the crypto world, we saw this with the early days of offshore exchanges. MiCA was supposed to bring everyone into a clean, well-lit room. But even within the EU, there are variations in how rules are interpreted.
The European Council’s new focus suggests they are worried about a race to the bottom. By giving ESMA the power to step in when a firm’s activity has a cross-border dimension, they are effectively neutralizing the advantage of picking a specific country for its perceived softness. They want a single set of eyes on the biggest players to ensure that a failure in one country doesn't trigger a domino effect across the Eurozone.
Technical Debt in Compliance
For those of us in the trenches, this highlights a massive piece of technical debt that most crypto projects ignore: compliance architecture. Most founders build the product first and treat the legal side as a wrapper. Under the new ESMA-led model, compliance needs to be baked into the stack.
If you are operating across 27 countries, you need real-time reporting capabilities that can satisfy an EU-level auditor. You can't rely on the manual, bespoke reporting that worked for a single national regulator. The move toward centralized supervision is a signal that the EU expects crypto firms to operate with the same institutional rigor as a Tier-1 bank.
The Skeptic's Take
Is this actually about safety, or is it about control? Probably both. The official line is that this protects consumers from firms that slip through the cracks of national oversight. The cynical take is that the EU is tired of national regulators having all the fun (and the fees) and wants to centralize the power in Paris, where ESMA is headquartered.
For the crypto industry, this is a double-edged sword. On one hand, direct ESMA supervision could provide even more clarity. You won't have to worry about a German regulator disagreeing with a French interpretation of the same law. On the other hand, it removes the flexibility that smaller national regulators often provide. It makes the barrier to entry significantly higher for anyone trying to become a major player.
What Builders Should Do Now
If you are currently planning an EU expansion, don't just look at the cost of getting a license in Poland or Portugal. Look at the long-term cost of being regulated by ESMA. The selective model means that if you are successful, you will eventually be bumped up to the big leagues. You need to hire compliance officers who understand EU-level mandates, not just local ones.
- Audit your cross-border strategy: Are you relying on a single license to carry you across the entire EU? Start modeling for stricter reporting requirements now.
- Monitor the ESMA thresholds: We don't have the final numbers on what constitutes a significant provider yet, but you should be watching for the user count and AUM metrics that trigger central oversight.
- Diversify your regulatory footprint: Don't put all your eggs in one jurisdictional basket if that jurisdiction is known for being an outlier. Stability is more valuable than leniency in the long run.
The honeymoon phase of MiCA is over. The reality of operating in a highly regulated, centralized environment is setting in. For builders who want to survive, the strategy has to shift from finding loopholes to building robust, transparent systems that can withstand the scrutiny of a central authority.
The era of the one-license-fits-all model isn't dead yet, but the European Council just put it on notice. If you're building for the long haul, you need to prepare for a world where your local regulator isn't the final boss—ESMA is.
Read the original at CryptoSlate →