Security in the crypto space is often discussed in terms of grand architectural failures or massive bridge exploits. But for those of us building on the ground, the most dangerous threats are usually the quiet ones—the small, technical oversights that bridge the gap between a user's web browser and their financial infrastructure. The latest update to Eclair, a major Lightning Network implementation, addresses exactly this kind of silent threat.
The Browser as a Trojan Horse
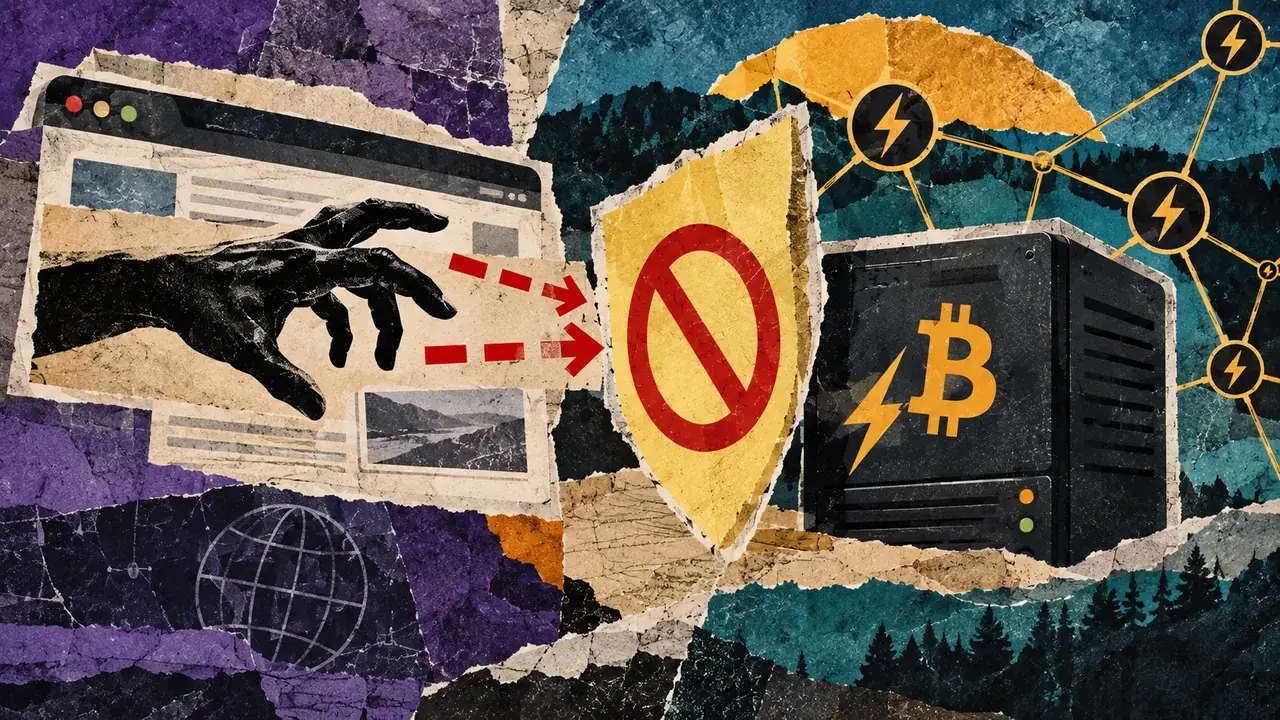
In the recent October 15 release, the developers behind Eclair quietly patched a vulnerability that could have allowed a malicious webpage to send commands directly to a user's Lightning node. This wasn't a flaw in the Bitcoin protocol itself, but rather a classic web-based attack vector known as cached-authentication exploitation. Essentially, if you had your Eclair node's API open and were authenticated in your browser, a separate, malicious site could potentially ride those credentials to issue instructions.
For a founder or a developer, this is a wake-up call regarding the 'convenience' we build into our interfaces. We want things to be seamless, but when 'seamless' means a background script can tell your node to open a channel or send a payment without your knowledge, we have a problem. The fix involves blocking these specific browser-based requests and requiring any direct browser interface to explicitly add a backend, rather than relying on ambient credentials.
Why This Matters for Builders
If you are building an application that interacts with the Lightning Network, you need to understand the relationship between the local environment and the web. Most users run their nodes on the same machines they use for daily browsing. This creates a shared security context that is incredibly difficult to sandbox perfectly.
The Eclair patch is a reminder that we cannot trust the browser's default security model to protect financial assets. When we build dashboards or management tools for nodes, we often use REST APIs. These APIs are powerful, and if they are accessible via standard browser requests (CORS), they are vulnerable. The move by Eclair to restrict these requests is a move toward a 'permission-by-default' stance that every crypto project should adopt.
The Risks of Cached Authentication
The core of this issue is how browsers handle identity. Once you log into a service, the browser often holds onto that session state. If an API endpoint doesn't strictly validate the origin of a request or requires specific, non-standard headers that a generic script can't easily replicate, it leaves the door open. In the context of a Lightning node, an attacker doesn't need to steal your private keys to ruin your day. They just need to convince your node to perform an action that benefits them—like sending a payment to a specific invoice.
This is why the founders of these protocols are constantly playing catch-up with web standards. The web was built for sharing documents, not for securing peer-to-peer financial nodes. As builders, we are essentially trying to bolt bank-grade security onto a platform that was designed to be open and interconnected.
A Founder’s Perspective on Node Security
When I look at this from a founder's perspective, I see a recurring theme: complexity is the enemy of security. The more features we add to make nodes easier to manage via the web, the more surface area we give to attackers. We have to ask ourselves if every node really needs a web-accessible API enabled by default, or if we should be pushing users toward more isolated management tools.
The Eclair team did the right thing here by tightening the screws. They recognized that the convenience of a web UI wasn't worth the risk of a cross-site attack. For those building the next generation of Bitcoin apps, the takeaway is clear: don't rely on the user's browser to keep their funds safe. Assume the browser is compromised and build your authentication and request validation layers accordingly.
Practical Steps for Development Teams
- Audit your API endpoints: Ensure that no sensitive actions can be triggered by a simple GET or POST request from a third-party domain.
- Implement strict CORS policies: Only allow requests from trusted origins, and even then, be skeptical.
- Move away from ambient auth: Require explicit tokens or headers for every single command that moves money or changes state.
- Educate the user: Make sure they know that running a node and browsing the 'dark corners' of the web on the same machine carries inherent risks.
The Bigger Picture
This isn't just an Eclair issue; it's a structural challenge for the entire Lightning ecosystem. As we push for mass adoption, we are bringing in users who don't understand the nuances of browser security or network isolation. They expect their 'Bitcoin bank' to be as safe as their traditional banking app, not realizing that their browser is a massive hole in their defenses.
We are still in the early stages of figuring out the best practices for local node management. Whether it's through better sandboxing, dedicated hardware interfaces, or simply more robust API security like Eclair just implemented, we have to stay ahead of these basic web exploits. If we can't secure a node against a simple malicious webpage, we have no hope of scaling this technology to the billions of people who actually need it.
The most dangerous vulnerabilities aren't the ones that break the protocol, but the ones that exploit the tools we use to access it.
The lesson here is simple: simplicity and isolation are your friends. If you're building in this space, take a page out of the Eclair playbook. Be honest about the limitations of the web, be skeptical of 'easy' authentication, and always prioritize the safety of user funds over the smoothness of the UI. It’s better to have a slightly clunky interface than a drained wallet.
Read the original at CryptoSlate →