The Quantum Boogeyman Gets a Reality Check
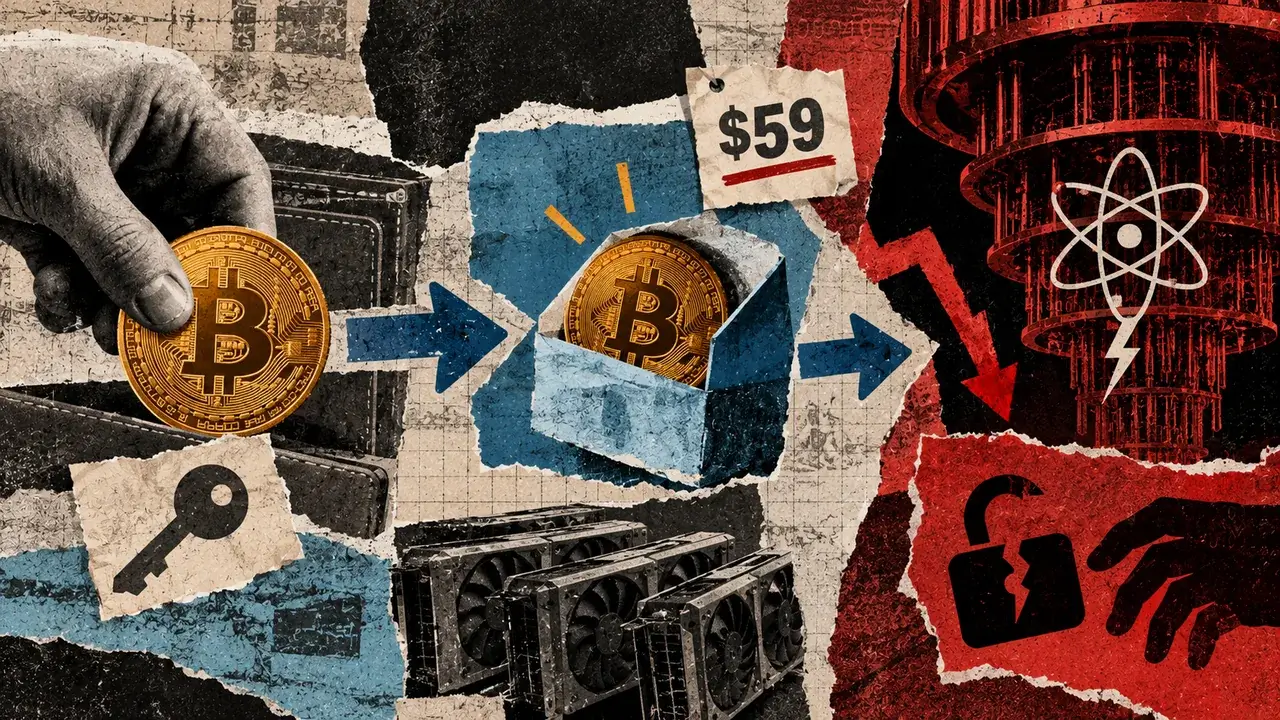
For years, the threat of quantum computing has been the ultimate "doomsday clock" for Bitcoin. The theory is simple: one day, a computer will become powerful enough to crack the elliptic curve cryptography that secures your private keys. If that happens, any Bitcoin sitting in an older address format is essentially up for grabs.
New research is starting to change the math on how we defend against this. Recent developments in GPU-accelerated computation have reportedly dropped the cost of implementing Quantum-Safe Bitcoin (QSB) protections by roughly 82%. While that sounds like a win for the little guy, the reality for builders and long-term holders is significantly more nuanced.
The 6 Million BTC Problem
We need to talk about the scale of the vulnerability. Roughly 6 million BTC are currently sitting in "P2PK" (Pay to Public Key) or older P2PKH addresses where the public key is already known to the network. In modern Bitcoin addresses, your public key isn't revealed until you actually spend from the wallet. But for these older accounts—many of which belong to Satoshi or early pioneers—the map to the gold is already printed on the wall.
If a quantum actor emerges, these 6 million coins are the first targets. The race isn't just about making Bitcoin quantum-resistant; it is about making that transition affordable enough that legacy holders (or their heirs) actually bother to move their funds before the clock hits zero.
GPU Acceleration and the Cost of Defense
The breakthrough here isn't a new mathematical formula, but rather a more efficient way to process the heavy lifting required for quantum-safe signatures. By leveraging specialized GPU computation, researchers have found a way to prepare QSB spends much faster and cheaper than previously thought possible.
For a founder building in this space, this is a signal that hardware optimization is catching up to theoretical threats. We often assume that as computers get faster, the attackers win. But this research shows that the same hardware advancements can be used to build the shields. An 82% reduction in cost means that protecting a legacy stash is no longer a luxury reserved for whales.
The Bottleneck: Miner Access and Signatures
Here is where I get skeptical. Even if the computation is cheaper, the implementation remains a massive hurdle. Current quantum-safe proposals often rely on conventional funding signatures to get the process started. You are essentially using a regular, vulnerable door to build a vault behind it. If the attacker hits you during that transition, the quantum-safe shield doesn't matter.
Furthermore, these spends often require direct miner cooperation or specific network conditions that don't exist in the current mempool environment. As a builder, you have to ask: who controls the gateway? If protecting your Bitcoin requires a specialized relationship with a mining pool, we haven't solved the problem; we've just moved the trust requirement from math to politics.
What This Means for Founders
If you are building wallets, custody solutions, or Layer 2s, you can't ignore the legacy debt of the Bitcoin network. We have trillions of dollars in value secured by math that has a shelf life. The fact that the "protection tax" is dropping is good news, but it doesn't change the fact that the UX for migrating to quantum-safe standards is currently terrible.
The opportunity for founders isn't just in the cryptography—it is in the abstraction. The first team to build a seamless, one-click migration path for legacy addresses that utilizes these cheaper GPU-backed protections will own the security market for the next decade.
The Takeaway
Quantum computing is still a "when," not an "if," but we are seeing the tools for defense become more accessible. An 82% drop in cost is a great headline, but the friction of moving funds and the reliance on traditional signature schemes remain the real vulnerabilities. Don't wait for a hardware miracle; the software and the network consensus are where the real battles will be fought. For now, the best defense is staying informed on how these new computational efficiencies can be integrated into your stack without adding central points of failure.
Read the original at CryptoSlate →